TL;DR
How do I keep my AI API key from being stolen and run up?
Hackers at app host Railway hunted for AI keys and ran up an estimated $740,000 in charges. Any key you've saved on a host or in code can be spent by whoever finds it. Make a new key and delete the old one, use one key per project, and set spending limits and billing alerts with every AI provider.
Why is a stolen AI key so expensive?
An API key is a long password that lets an app use an AI service, such as OpenAI, Anthropic or Google Gemini, and charge it to your account. Whoever holds the key can run as many requests as they like, and the bill comes to you. In practice, an AI key works like a credit card number with no PIN.
That's exactly what thieves were after in October. Railway, an app host popular with solo builders and people who make apps with AI help, says in its incident report that the attacker "was specifically targeting AI provider credentials" and likely passed them on for resale. Railway estimates unauthorized spending on the stolen keys reached about $740,000. The full story of the Railway breach covers the timeline and who was affected.
Railway is also clear about scale. At most 1.85% of its workspaces, about 100,000, could have had saved settings decrypted, and Railway calls that an upper bound, not a count of victims. Its forensics showed no access to customer databases. Railway also says the break-in was "one of a series of attacks on platforms that hold AI keys," naming OpenCode, Warp and Fireworks AI as companies that disclosed similar thefts in October.
Was my AI key stolen in the Railway breach?
Maybe not, but don't wait to find out. Railway says it emailed customers it judged to be at high risk, and it asked GitHub, GitLab, Anthropic, OpenAI, OpenRouter, SpaceXSI, Google and Stripe to revoke keys that might have been exposed. Because it couldn't yet tell which keys were exposed, it sent providers hashes of every key it held.
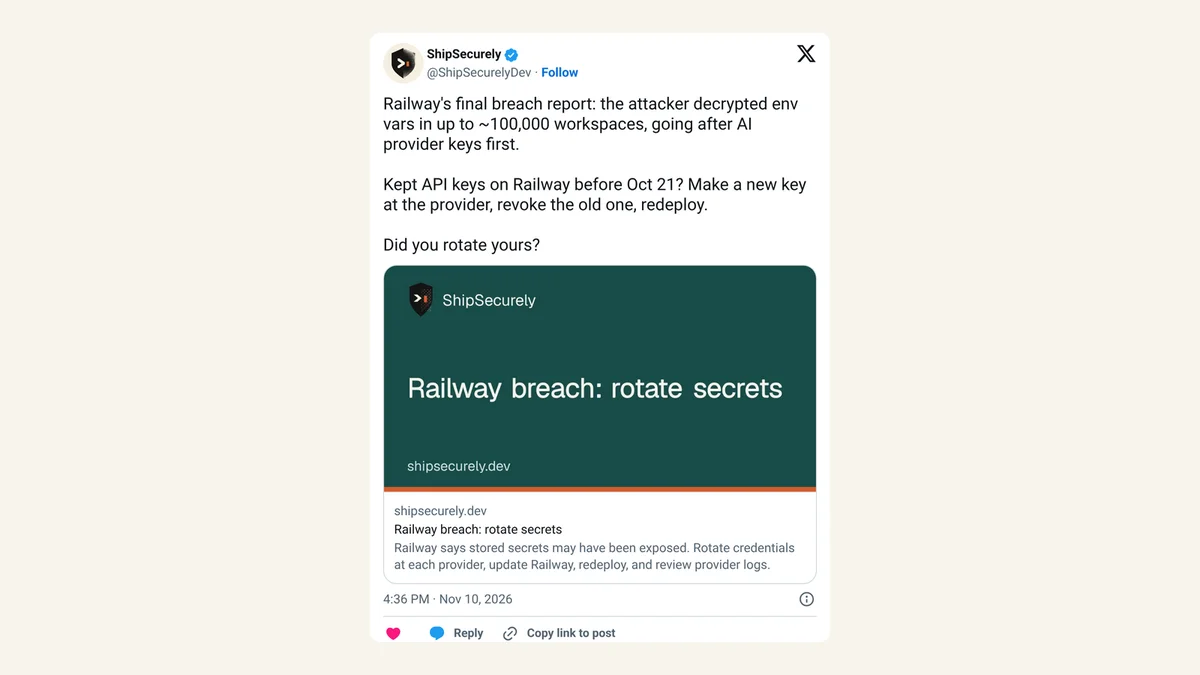
If you kept AI keys in Railway settings before October 21, treat them as burned. One builder on X put the fix in one line: "Make a new key at the provider, revoke the old one, redeploy" (ShipSecurely on X). Then look at your usage for any spending you don't recognize.
If you find charges you didn't make, Railway asks customers to report them through the form linked in its incident report. Its report lists what each provider is doing. AWS Bedrock and Google Gemini cover fraud under their own refund policies. OpenAI and SpaceXSI review claims case by case. Railway says it's covering Anthropic and OpenRouter costs for now, and will cover losses any provider won't refund.
How do I lock down my AI keys?
Five steps, about 15 minutes the first time. They work wherever you host.
1. Replace keys the right way. Make a new key at the provider, put it where your app reads it, check the app still works, then delete the old key. Pausing or hiding a key isn't enough. A Reddit thread in r/cybersecurity is titled "PSA: Pausing your API key does not stop an attacker who already has it." Delete it.
2. Give every project its own key. One key for your website chatbot, another for your invoice automation, another for trying out ideas. When one leaks, you replace one key, and your usage page shows which project the strange charges came from.
3. Set a spending limit and a billing alert at every provider. Most AI providers let you set a monthly budget, a usage cap or an email alert in their billing settings, and the names differ from one company to the next. Set the cap a little above what you normally spend. A thief can still burn through that, but not through $740,000.
4. Keep keys out of chats, code and screenshots. Store them in your host's secret settings (often called environment variables, saved values your app reads without showing them in the code). Never paste a real key into an AI chat, a public code folder, a support ticket or a screen recording. Our 10-minute check for keys you've pasted into AI tools walks through finding the ones already out there.
5. Read your host's security emails. Breach notices from a host are easy to mistake for marketing. When one arrives, replace the keys stored there that day.
Anyone who finds your AI key can spend your money until you delete it.
What if my whole team shares one ChatGPT plan?
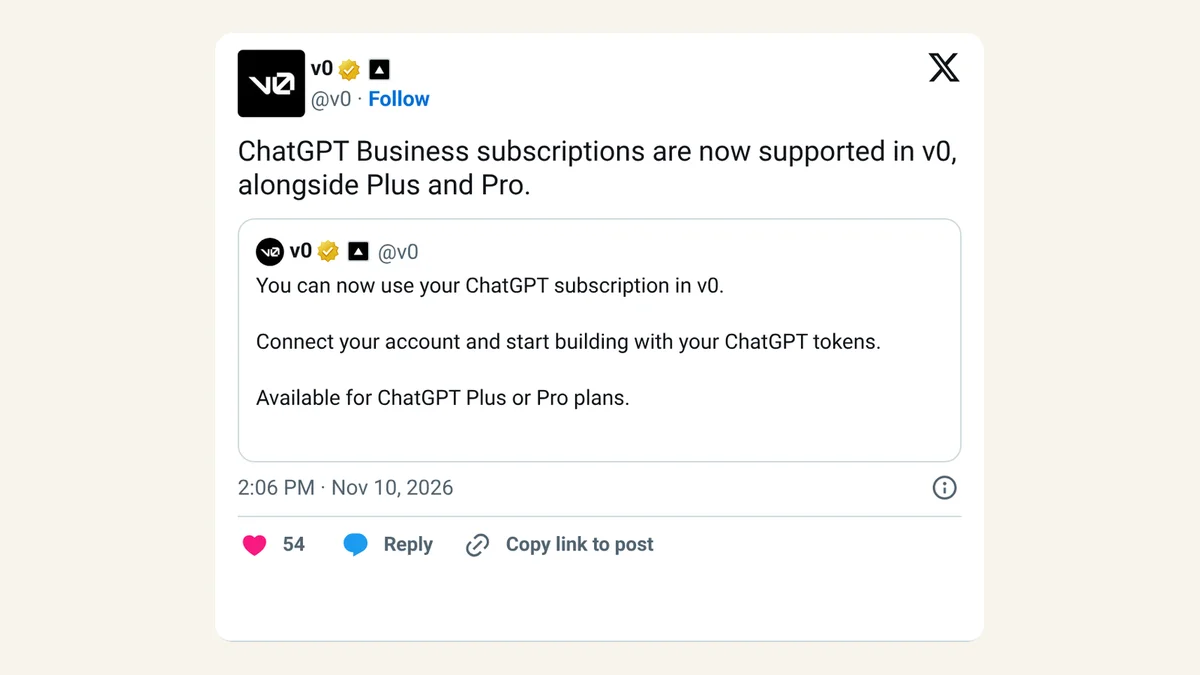
Shared plans are getting their own controls. OpenAI now lets some apps, including Notion, Vercel and Warp, run on your ChatGPT plan instead of a separate key. Its help page says that usage "counts toward your existing plan limits" and that connecting an app "does not add a new allowance."
You can cap each app yourself. OpenAI's help page says to open Settings > Usage in ChatGPT and set each app's weekly limit as a percentage of your plan. Business admins can set a workspace-wide percentage at admin.openai.com under Usage limits. A cap like that won't stop a breach, but it keeps one app from eating the whole team's allowance.
Is it worth the hassle for a small side project?
We think so. Thieves went after a host that stores keys for many people at once, so they don't care how small your project is. Your key is worth the same to them either way.
The habits are cheap. A spending cap takes two minutes. Separate keys take five. The tedious part, replacing a key, gets easier each time you do it, and people have been doing it in a hurry for a while. Another Reddit thread, in r/SideProject, describes a builder up at 2am replacing keys after a different host was hacked, "before hackers drain my AI budget" (r/SideProject). Do it on a calm afternoon instead.
FAQ
Does deleting my old key break my app?
Only if the app still uses it. Put the new key in place first, check the app works, then delete the old one.
Will my AI provider refund charges from a stolen key?
It depends on the provider. For the Railway breach, Railway says AWS Bedrock and Google Gemini cover fraud, OpenAI reviews case by case, and Railway covers what providers won't.
Is a spending limit the same as a billing alert?
No. An alert emails you when spending passes a set amount. A limit stops or blocks usage at that amount. Use both where your provider offers them.
Do I need a key at all if I only use the ChatGPT app?
No. Keys are for apps, bots and automations that call an AI service. Chatting in ChatGPT, Claude or Gemini doesn't use one.
Sources
- Railway: Incident Report: October 21st Security Attack — November 10, 2026 (last updated 18:02 UTC). Targeting of AI keys, ~$740,000 estimate, up to 1.85% (~100,000) of workspaces as an upper bound, revoke requests, refund policies by provider, similar thefts at other platforms.
- OpenAI: Sign in with ChatGPT — plan usage in other apps, Settings > Usage app limits, Business admin usage limits.
- ShipSecurely (@ShipSecurelyDev) on X — November 10, 2026.
- r/cybersecurity thread title via Google search results: PSA: Pausing your API key does not stop an attacker who already has it.
- r/SideProject thread title via Google search results: Vercel got hacked, but it's me up at 2am rotating keys before hackers drain my AI budget.