TL;DR
What happened in the Railway breach?
An attacker broke into Railway, an app-hosting service, and stole saved AI keys from up to 100,000 workspaces. A stolen key lets strangers run up AI charges on your account. If you kept AI keys on Railway before October 21, make new ones, delete the old ones and report odd charges.
What happened at Railway
Railway hosts websites, apps and bots for developers, including plenty of solo builders who make apps with AI help. On Tuesday, November 10, 2026, it published its full report on an attack that ran from October 20 to October 21.
Railway says the attacker found a flaw in its build system, the part that turns your code into a running app, and broke partly out of it. From there they picked up internal passwords, copied Railway's own code to look for more weak spots, and reached the database holding customers' saved settings. Those settings, called environment variables, are where apps usually keep secrets like API keys. An API key is a long password that lets an app use a paid service such as OpenAI or Anthropic, and the bill goes to whoever owns the key.
Railway says the attacker was "specifically targeting AI provider credentials." Database logs show them searching for rows whose names matched AI key patterns, and favoring customers with lots of saved settings. Railway believes the keys were passed on to resale operations that sell cheap access to AI models.
How many Railway users were affected?
Railway's logs show that at most 1.85% of workspaces, about 100,000, could have had saved settings decrypted. Railway calls that an upper bound, so "up to" 100,000 is the safe reading, and many of those workspaces may have lost nothing.
Other numbers from the report:
- ~$740,000: Railway's estimate of unauthorized AI spending on the stolen keys.
- 1,852 users: had linked-account tokens decrypted, including GitHub connection tokens and users' own keys for AI agents. Railway reset every one and found no logins to Railway accounts using stolen credentials.
- 353 builds: had their stored history read, including saved settings.
- October 22 to November 2: new sign-ups were paused while Railway rebuilt its systems.
Railway says its forensics didn't show that customer databases were accessed. Running apps stayed online, though some broke for a while when owners revoked keys and couldn't redeploy until builds came back.
Who pays for the stolen AI charges?
Railway says it's asking every AI provider to refund the unauthorized usage, and it will cover the charges itself where a provider says no. Its report lists where things stood on November 10:
| Provider | What Railway says happens |
|---|---|
| AWS Bedrock | AWS's fraud policy applies; refunds started |
| Google Gemini | Google's fraud policy applies; refunds started |
| OpenAI | Open a support request, then give the case ID to Railway support; reviewed case by case |
| SpaceXSI | Contact Railway support with the claim; reviewed case by case |
| Anthropic | Talks ongoing; Railway is covering the costs for now |
| OpenRouter | No refund under its terms; Railway is covering the costs |
Railway asks anyone with charges they didn't make to report them through the form linked in its report.
Why did hackers want AI keys?
A working AI key is close to free money. Whoever holds it can run expensive AI jobs and send the bill to someone else. Railway says the misuse it has seen ranged from coding agents to AI training work, which fits keys being resold through services that relay access to AI providers.
Railway also says it wasn't the only target. It names OpenCode, Warp and Fireworks AI among companies that disclosed similar thefts between October 6 and October 23, and calls this "one of a series of attacks on platforms that hold AI keys."
Is Railway safe to use now?
Railway says every weakness the attacker used is now closed. Each build runs in its own short-lived virtual machine, decryption is logged and limited to one service, and its internal deploy pipeline needs two-factor approval for sensitive steps. It has also filed a complaint with the FBI's IC3 and brought in an outside forensics firm.
Railway also answers why users heard so late, saying it "can always be faster." It warned AI providers first so they could revoke keys, then held off on a broad notice while it confirmed who was hit. It says future incidents will have a fixed deadline, after which everyone gets told regardless.
X reactions
Two builders boiling the report down to one habit:
Hackers stole AI provider keys and ran up roughly $740K in unauthorised spend. Railway says the October breach targeted keys for resale. Not a model problem, a secret-in-one-place problem. When did you last rotate yours?
— 未晚 (@weiwan_ok) November 11, 2026
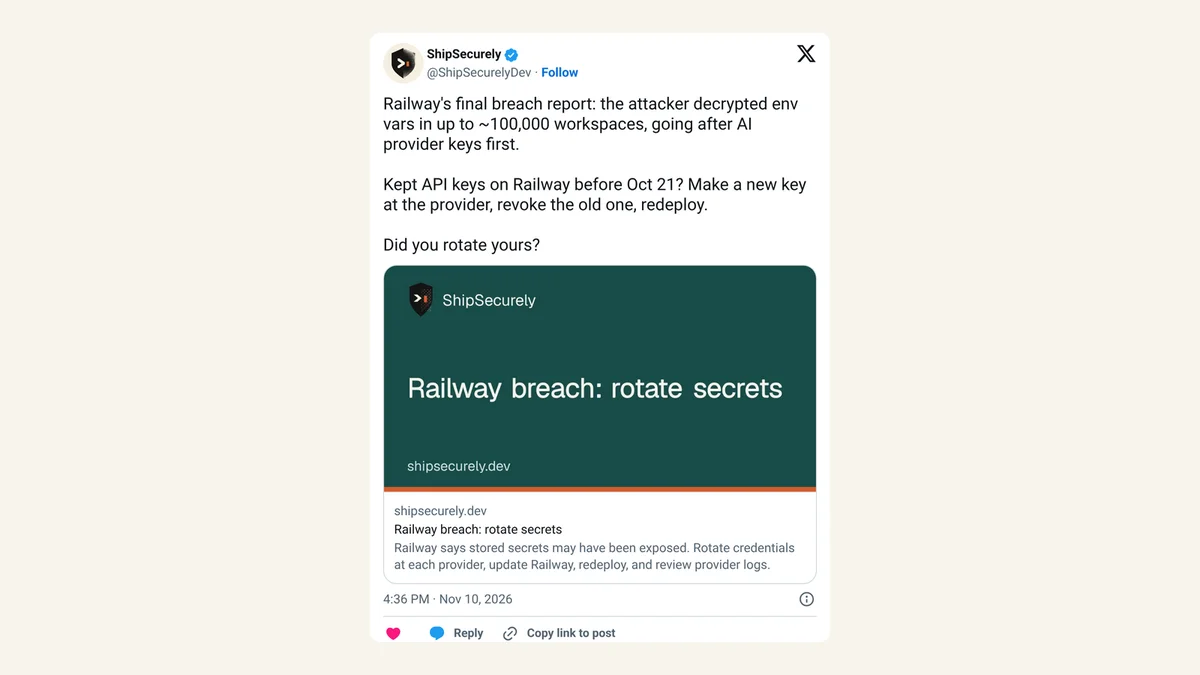
Railway's final breach report: the attacker decrypted env vars in up to ~100,000 workspaces, going after AI provider keys first.
— ShipSecurely (@ShipSecurelyDev) November 10, 2026
Kept API keys on Railway before Oct 21? Make a new key at the provider, revoke the old one, redeploy.
Did you rotate yours?
https://t.co/Gr294gG3uQ
Our take
Railway's report is unusually open. It names the flaws, the timeline, the dollar figure and which providers are refunding, and it promises to cover what they won't. That's how a company should handle a breach, even if users heard about it later than they should have.
The bigger lesson reaches past one host. AI keys have become one of the most valuable things a small app stores, and attackers know where people keep them. If you built something with AI help this year, your app probably holds a key that can spend real money. Treat it like a credit card number: one per project, a spending cap at the provider, and a fresh one whenever a service you use reports a breach.
— Artificially Nerdy
What to do now
- Kept AI keys on Railway before October 21? Make a new key at each AI provider, put it in your app, redeploy, then revoke the old key.
- Check your AI bills for October 20 onward and look for usage you don't recognize.
- Report charges you didn't make through Railway's form, and for OpenAI, open a support request first and pass the case ID to Railway.
- Set a spending limit and billing alerts at every AI provider you pay, so a stolen key hits a ceiling fast.
- Use one key per project so a leak in one app doesn't drain the rest. Our guide covers how to rotate API keys step by step.
- Not a Railway user: still worth a quick look at where your AI keys live. Read our guide on how to protect an AI API key from theft for a short checklist.
FAQ
Were my Railway databases stolen?
Railway says its forensics didn't show that customer databases were accessed. The attacker went after saved settings, mainly AI keys, though one query also matched cloud, database and payment credentials.
Did Railway email affected users?
Railway says it emailed customers it judged to be at high risk and notified all 1,852 users whose linked tokens were reset.
Do I need to change my Railway password?
Railway invalidated every user session on October 21, so everyone had to log in again. It found no logins using stolen credentials. Changing a reused password is still sensible.
Was this the first attack like this?
No. Railway says OpenCode, Warp and Fireworks AI disclosed similar AI key thefts in October.
Sources
- Railway: Incident Report, October 21st Security Attack — November 10, 2026, last updated 18:02 UTC (1:02pm ET). Timeline, attacker's target, 1.85%/~100,000 workspaces, ~$740,000 estimate, 1,852 users, 353 builds, sign-up pause, provider refund policies, fixes.
- 未晚 on X — November 11, 2026, 3:38am ET.
- ShipSecurely on X — November 10, 2026, 4:36pm ET.